Your SA Business Was Hacked. Here Is What the POPIA Breach Notification Process Actually Looks Like.
The Clock Is Already Running
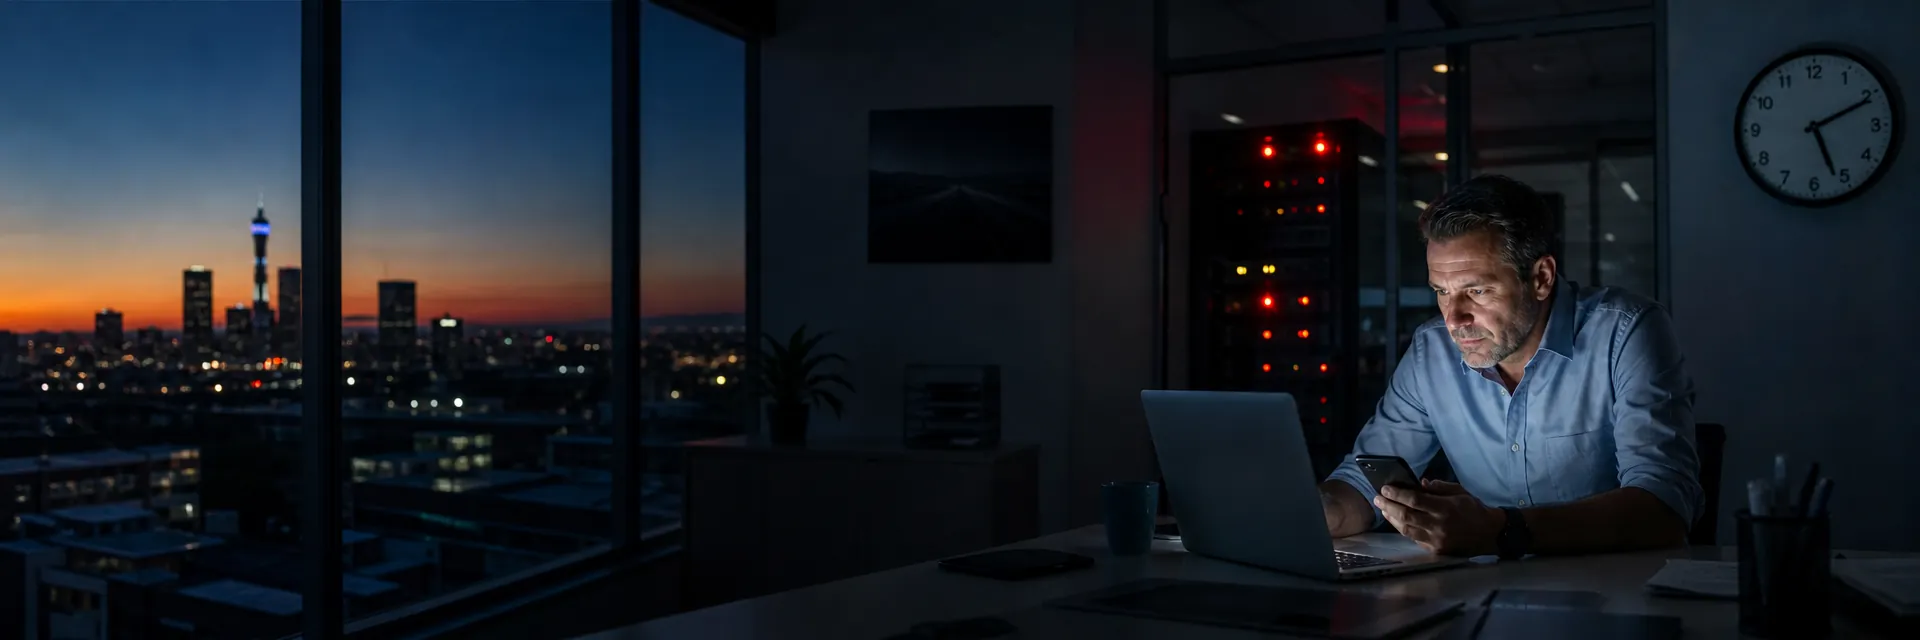
It is 17h10 on a Friday in Johannesburg. The bookkeeper at a 38-person logistics company tries to open the payroll folder and gets an access error. Then another. Then a popup appears on the file server demanding payment in cryptocurrency.
Within minutes it is clear: the business has been hit by ransomware. Employee IDs, salary information, bank account numbers, and scanned copies of client contracts are stored on that server. And whether they know it yet or not, POPIA breach notification is now a legal obligation.
South Africa has one of the most active cyberattack landscapes in the world. The Information Regulator received 2,374 security compromise reports between April 2024 and March 2025, an average of 198 per month — and that figure rose to 284 per month by mid-2025.
Over 40% of all ransomware attacks on the African continent in the second half of 2024 targeted South African organisations. For an SME owner, it is no longer a question of whether a breach will happen. It is a question of whether the business is ready to respond when it does.
POPIA’s Section 22 sets out exactly what must happen after a security compromise.
The Act says notification must happen “as soon as reasonably possible” — and the Information Regulator’s own POPIA Awareness Training places the practical benchmark at ideally within 72 hours. Those are 72 calendar hours, not business hours. A Friday evening breach becomes a Monday evening deadline. Here is what that process looks like in practice, step by step.
What Triggers the POPIA Breach Notification Obligation
The legal trigger is not certainty. POPIA requires notification when there are reasonable grounds to believe that personal information has been accessed or acquired by an unauthorised person.
That is an important distinction, because most breaches are chaotic in the first few hours. You may see encrypted files, unusual outbound traffic, disabled antivirus, or suspicious admin logins without yet knowing the full extent of what happened.
The scope of what counts as a security compromise is deliberately wide. A sophisticated ransomware attack, a phishing email that exposed a staff member’s credentials, an employee accidentally forwarding a client database to the wrong address, or a third-party supplier whose systems were compromised while holding your data — all of these can trigger the Section 22 notification obligation.
Critically, if your cloud backup provider, payroll software supplier, or any other operator was the actual point of entry, the duty still rests with you as the responsible party. The Dis-Chem enforcement notice — issued after a brute-force attack on a third-party service provider exposed 3.6 million records — made that clear. The business whose data was compromised is responsible for notifying affected people, regardless of where the breach originated.
Hours 0–4: Contain Before You Report
The first priority is containment. In the logistics company scenario, this means disconnecting the affected file server from the network, disabling remote access, and isolating any machines showing unusual behaviour.
What it does not mean is wiping, rebooting, or deleting anything. That instinct to “clean up” can destroy the evidence the business will need for both the regulator notification and any police report.
The company’s Information Officer must be notified immediately. Under POPIA, every business that processes personal information is required to have a designated Information Officer — by default, the head of the business unless the role has been formally delegated.
The IO is personally responsible for the POPIA breach notification submission. If that role has never been formally assigned or registered with the Regulator, those hours before an incident become critical groundwork that cannot be done during one.
By the end of the first four hours, the business should have a working picture of the incident: which systems were affected, what categories of personal information were stored there, how many people may be impacted, and what the likely attack vector was. This information shapes the notification and the response.
Hours 4–24: Submitting the POPIA Breach Notification to the Information Regulator
As of 1 April 2025, all security compromise notifications must go through the Information Regulator eServices portal. The old email-based and PDF form processes have been replaced. Submitting by email may be treated as non-compliant.
The IO logs into the portal and files the notification with the facts available at the time. The form asks for: the date of the compromise, the date of reporting, the type of compromise, the categories of personal information involved, the approximate number of data subjects affected, and any explanation for delay.
Importantly, the notification does not have to be complete. If not all facts are known yet, what is known must be submitted — it can be updated as the investigation develops.
Once submitted, the Regulator will issue a reference number confirming receipt. The IO should also consider whether to open a criminal case with SAPS, particularly for ransomware incidents where evidence of extortion exists. For the logistics company in this scenario, both steps apply.
One thing that stops businesses cold at this stage: not having the IO registered on the portal before the incident. That registration cannot be done during a breach for the first time.
If it has not been done, the notification process stalls. This is why preparation before an incident matters — not just technically, but procedurally.
Hours 24–72: Notifying the People Whose Information Was Compromised
The notification obligation does not stop with the Regulator. The business must also notify the affected data subjects — in this case, the logistics company’s employees, and potentially its clients whose contract documents and personal details were stored on the server. The only exception is if the Regulator or law enforcement specifically requests a delay to avoid compromising a criminal investigation.
The message to affected people must be practical and clear. Section 22(5) sets out what it must include: a description of what happened and its likely consequences; what the business has done or plans to do; and what the affected individual should do to protect themselves. In plain terms, that means telling staff members to change their passwords, monitor their bank accounts, watch out for phishing attempts that may use their leaked information, and place fraud alerts where relevant.
If the identity of the attacker is known, that must be included too.
Notification can be sent by email, letter, prominent notice on the business website, or media publication — or by a method the Regulator directs. If a website notice is used, the Information Regulator’s guidance recommends keeping it live for 30 to 90 days. The method chosen should match the scale of the incident and whether individual affected people can be directly identified and contacted.
What Happens If You Do Not Comply
The penalties for failing to handle POPIA breach notification correctly are real and are being enforced. The Information Regulator can issue administrative fines of up to R10 million without going to court.
For serious offences — such as obstructing the Regulator or destroying evidence — directors and Information Officers face up to 10 years’ imprisonment. For lesser offences, up to 12 months. Under Section 99, affected individuals can also bring civil claims for damages against the business directly.
South African enforcement is no longer theoretical. The Department of Justice was hit with South Africa’s first POPIA fine — R5 million — after failing to comply with an enforcement notice following a 2021 ransomware attack.
Lancet Laboratories was fined R100,000 after failing to notify affected data subjects following multiple security compromises. Dis-Chem received a formal enforcement notice for the same failure after the breach of 3.6 million records through a third-party supplier.
The Lancet case is particularly relevant for SMEs: a private healthcare business, not a government department, fined for the failure to notify data subjects specifically. The message from the Regulator is consistent — no organisation is too small, and the failure to notify is a fineable offence in its own right, separate from the breach itself.
The Single Biggest POPIA Breach Notification Mistake SMEs Make
Most SMEs do not fail this process because they ignore the law.
They fail because they have never rehearsed what to do in the first four hours. When a breach lands on a Friday afternoon, the questions pile up fast: Who is the IO? Are they registered on the portal? Do we have a log of what personal information sits on which system? Who approves customer communications? Who calls the lawyer?
Without clear answers to those questions before an incident, the 72-hour window compresses very quickly. Evidence gets lost. The notification stalls. Data subjects do not get told in time.
And the business finds itself in the position of having to explain those failures to the Regulator — at which point the fine is no longer a theoretical risk.
A practical incident response plan, assigned roles, a registered IO, and a tested escalation process are not expensive to put in place. But they are almost impossible to improvise under the pressure of a real breach.
The businesses that come through these incidents best are not necessarily the ones with the most sophisticated technology. They are the ones who knew what to do next.
How Wired IT Helps You Respond Fast
When a breach hits, every hour matters for both business continuity and for Section 22 compliance. Wired IT works with South African SMEs to make sure the technical and procedural foundations are in place before a crisis arrives — and to provide rapid response support when one does.
That means helping businesses strengthen endpoint detection, lock down email environments, maintain usable and tested backups, and monitor for signs of compromise before they escalate. It also means working through the procedural steps: making sure the Information Officer role is properly assigned, that incident response responsibilities are documented, and that the business is not discovering these gaps at 17h00 on a Friday for the first time.
When a breach does occur, faster technical containment means cleaner evidence, a clearer notification, and less disruption to the business while the investigation runs. The logistics company in this scenario had a recoverable situation — but only if the right actions happened in the right order at the right time. If your business is not confident it could execute this process under that kind of pressure, that is worth addressing now, not later.
Find out how Cybersecurity as a Service can put the right protections and response capabilities in place for your business. Or if you are ready to talk through your current situation, get in touch with the Wired IT team directly.